Building Overexposed: understanding application exposure
Our first scanner read config files and missed what was running. We rebuilt it with the cloud inventory, a careful probe, and honest results.
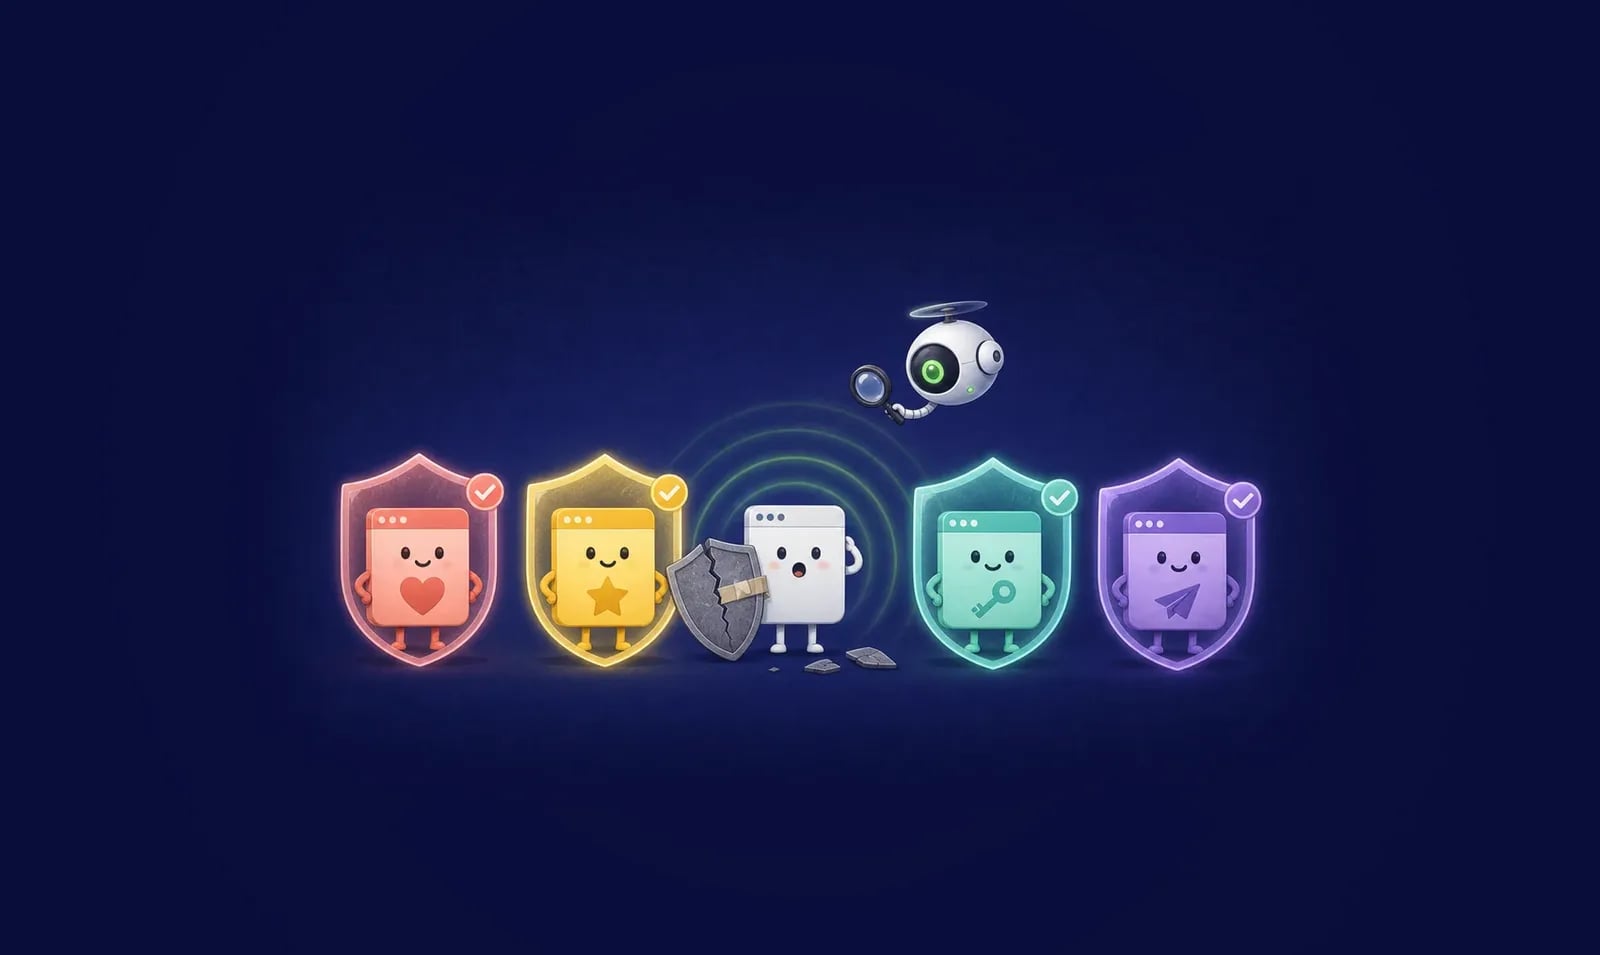
Which applications have internet exposure? Which endpoints allow access without authentication? Public access can be intentional. The challenge is to understand it and check whether it matches policy. Applications can run across many teams and cloud services. As these applications change, keeping track of their internet exposure and access controls requires regular checks.
We built a scanner called Overexposed to solve for this. It checks two types of internet-facing services: Kubernetes Ingresses on Google Kubernetes Engine (GKE), and Cloud Run services. It starts with the cloud’s inventory of deployed services, then checks whether each candidate allows access without a login. For every candidate endpoint, it gives a verdict and a reason.
How the scanner works
Overexposed runs on a schedule, and here’s what it does:
خواندن Shopify Engineering با پرو
این منبع جزو کتابخانه پرو است. همه منابع ویژه، ترجمه هوشمند و فیدهای شخصی را باز کنید.
منتشرشده در
Shopify Engineering
ادامه مطالعه
 Cloudflare Blog
 Netflix TechBlog