From Containers to Sandboxes: Developer Trust in the Agentic Era
The 2026 Stack Overflow Developer Survey shows only 7% of developers trust AI output for important decisions. Here’s what that means for running agents safely.
هوش مصنوعی۳ دقیقه مطالعه
موضوع
آسیبپذیریها، رمزنگاری، حریم خصوصی و دفاع.
The 2026 Stack Overflow Developer Survey shows only 7% of developers trust AI output for important decisions. Here’s what that means for running agents safely.
A recent InfoQ webinar examined operational challenges in deploying agentic systems. Key points included issues like semantic and embedding drift, which can lead to significant errors. Experts discussed the need for automated code reviews, continuous evaluation of models, and enhanced privacy measures. The session…
Identity alone doesn't guarantee a bot will behave responsibly. We are introducing a system to continuously evaluate whether Verified bots honor site preferences, like robots.txt and HTTP 429s, ensuring they remain accountable over time.
Andrew Martin discusses why AI security is fundamentally tied to Kubernetes security. He shares insights into the evolving AI threat landscape, covering non deterministic agent behavior, GPU supply chain vulnerabilities, shared compute risks, and practical defense strategies from prompt firewalling to agentic…
Software supply chain security company Chainguard has announced two beta products for running and testing code written by developers and AI agents. Chainguard Workspaces provides remote development environments based on hardened microVMs, while Chainguard Checks moves continuous integration into the development loop.…
This article provides a framework for asking the right architectural questions before an enterprise commits to an mDL provider or library. It shows which components can be abstracted safely, which trust boundaries must remain visible to the enterprise, what cryptographic and interoperability properties should be…
Founded in 2008, Stack Overflow’s public platform is used by nearly everyone who codes to learn, share their knowledge, collaborate, and build their careers.
Cloudflare Gateway and Data Loss Prevention have inherited the flexibility and power of Cloudflare Workers through our full stack integration with the Cloudflare Developer platform.
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This server side guide covers enabling DPoP and RFC 8693 Token Exchange, explains why 7.1 apps can silently stop enforcing DPoP until they call .dPoP(), and shows how to combine both into…
Learn the top AI agent security risks, from prompt injection to excessive autonomy and credential exposure, and how to contain them.
When strikes hit Yandex data centers, many assumed Russian bot operations went dark. Cloudflare data reveals that while search crawling stopped, malicious bots simply migrated to other networks.
The October 14, 2026 out of band security update for Next.js is now available
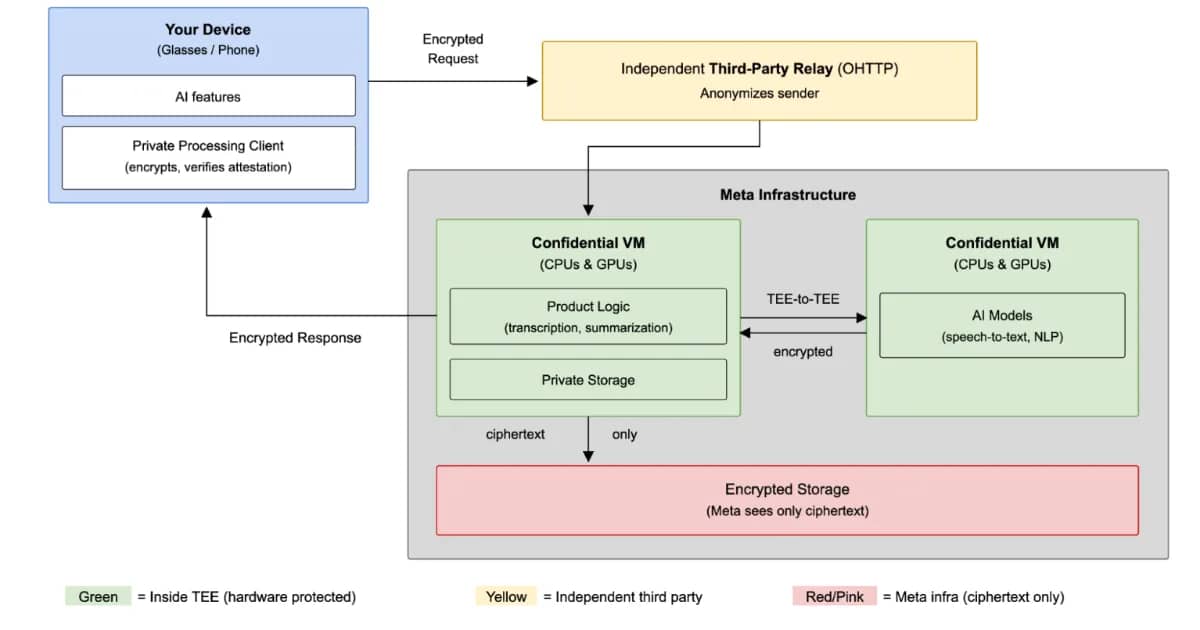
Meta has extended Private Processing to AI glasses, using confidential VMs, trusted execution environments, remote attestation, anonymous credentials, OHTTP routing, and TEE based storage to process AI workloads and persistent user context in the cloud. By Leela Kumili
With OpenAI Daybreak, SentinelOne cuts weeks of malware analysis to hours, creating capacity to investigate more threats.
Google has introduced support for local models in the Antigravity SDK, enabling developers to build and execute agentic workflows directly on their own machines, while retaining the flexibility to mix in cloud based models for higher level tasks. This approach gives developers greater control over data privacy,…
Anthropic opens its fifth Asia Pacific office in Singapore and signs an MOU with the government on AI safety, evaluation, and responsible adoption.
Block is building AI powered security with OpenAI. Its security team investigates threats faster and proposes patches in minutes.
In August, we launched the $1M hacker challenge for Vercel Sandbox , inviting security researchers to try and escape Vercel Sandbox. We also coordinated with cybersecurity experts Trail of Bits to review the source code and security architecture. Here is a summary of the challenge: 1,285 reports over two weeks…
Node.js® is a free, open source, cross platform JavaScript runtime environment that lets developers create servers, web apps, command line tools and scripts.
A critical remote command execution vulnerability in the Zimbra Collaboration Suite, identified as CVE 2026 73570, poses risks by allowing unauthorized access to mailbox data and credentials. This flaw, stemming from improper input sanitization, has been actively exploited. Organizations are advised to upgrade to…