Banking at machine speed: Securing access across cloud, AI, and hybrid environments
How can financial institutions manage access across cloud, AI, and hybrid environments while supporting compliance, auditability, and operational resilience?
Terraform 1.16 adds destroy time Actions and reusable imports in child modules, keeping more infrastructure lifecycle operations in Terraform.
The Terraform provider for Google Cloud 8.0 builds on expanded infrastructure discovery workflows, modernizes provider defaults, removes support for retired Google Cloud services, and improves consistency between Terraform configurations and Google Cloud APIs.
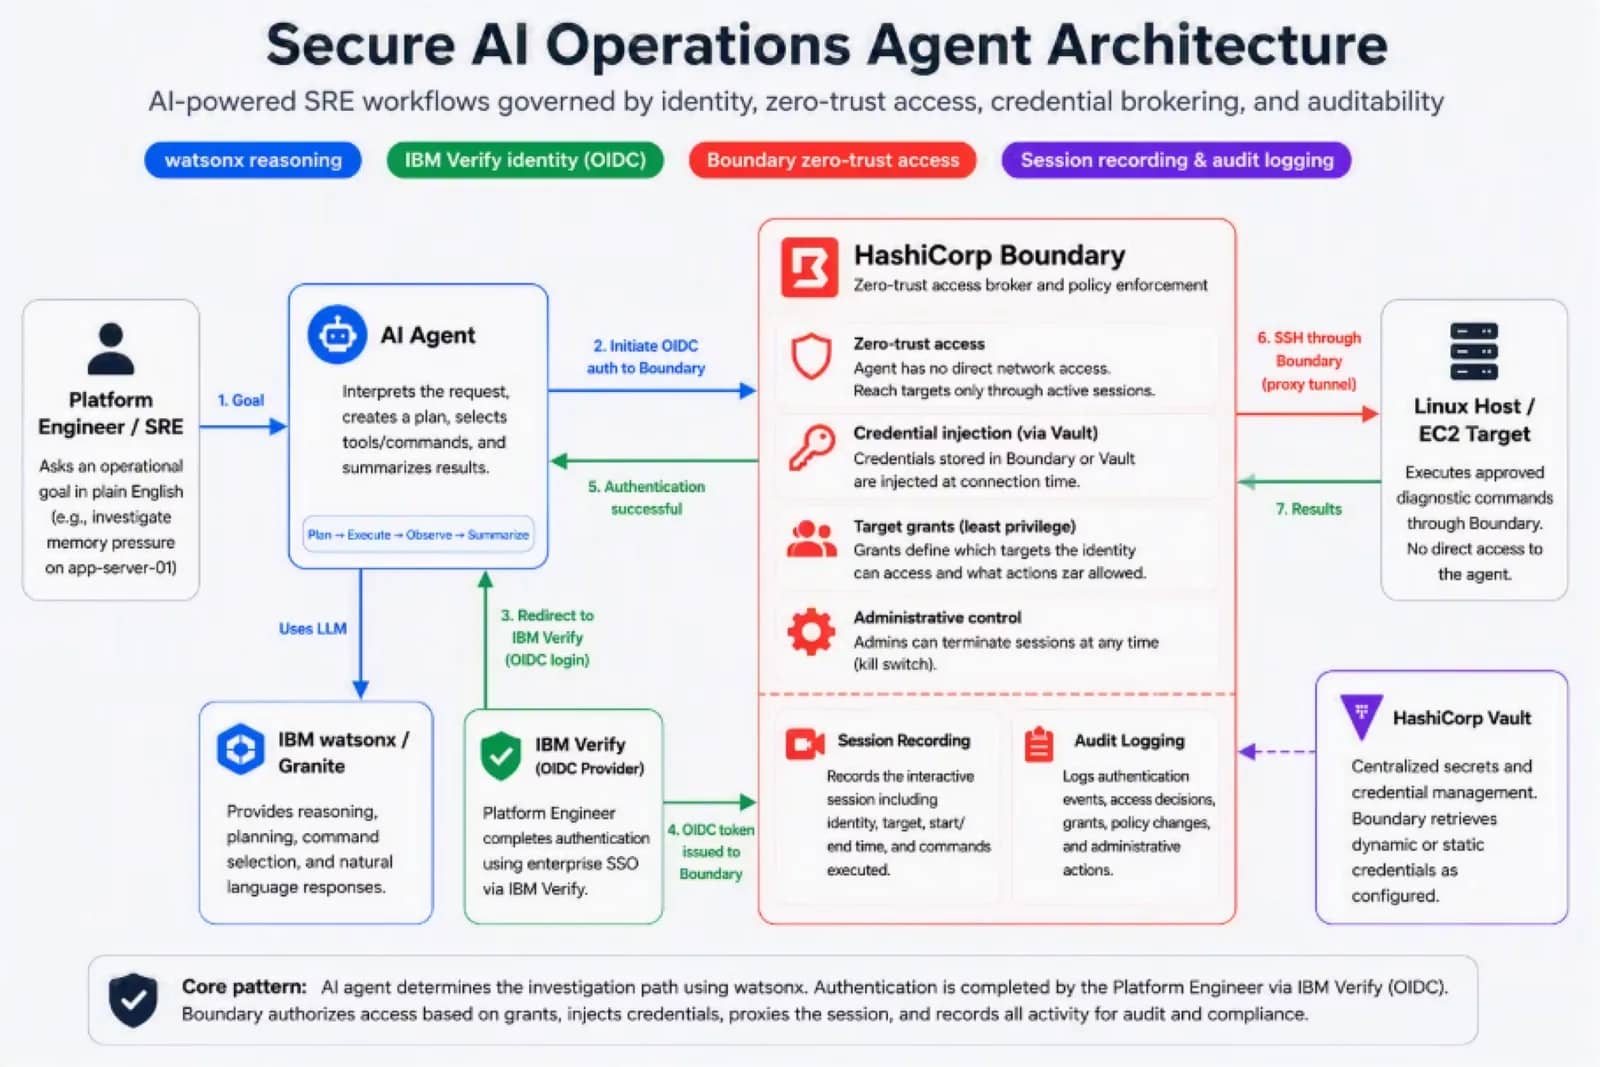
Enable AI agents to securely access your resources while operating within enterprise identity, access, and audit controls.
HCP Vagrant will be deprecated in 2026. Users should begin planning migrations as box creation, support, and operations are phased out.
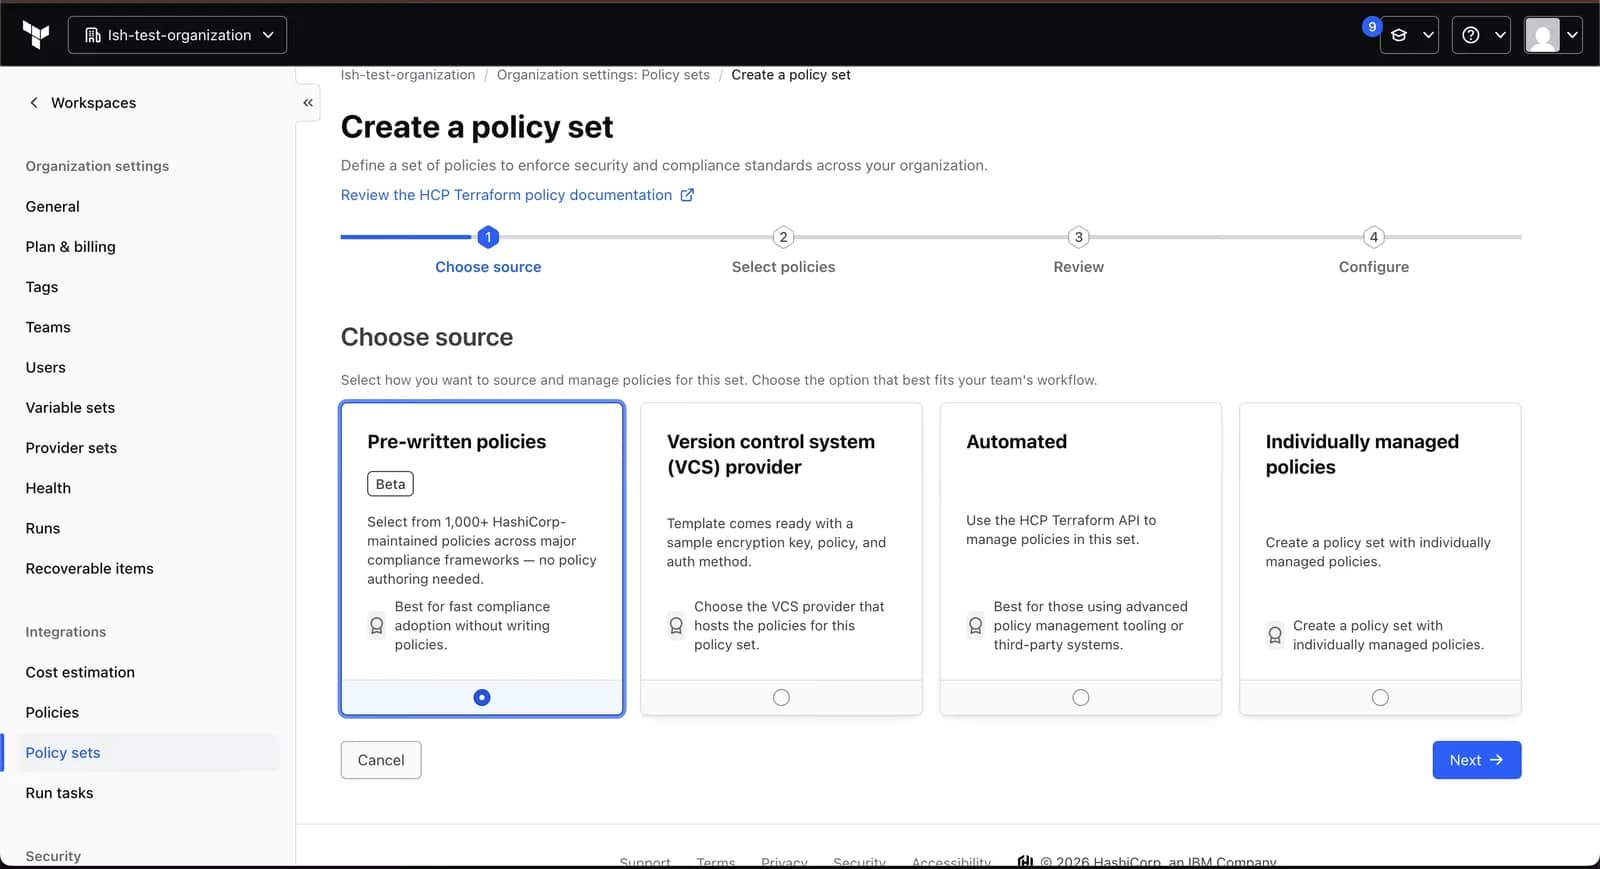
Teams can now browse HashiCorp managed pre written policies, add them to a policy set, and apply common compliance guardrails directly in HCP Terraform.
Learn how intent driven workflows introduce a new interaction model for IBM Terraform for Z and LinuxONE, helping organizations modernize infrastructure operations through guided, repeatable agentic workflows.
Gain deeper visibility into your HCP Terraform managed estate by pulling metrics from a single Prometheus endpoint into your data visualization tools.
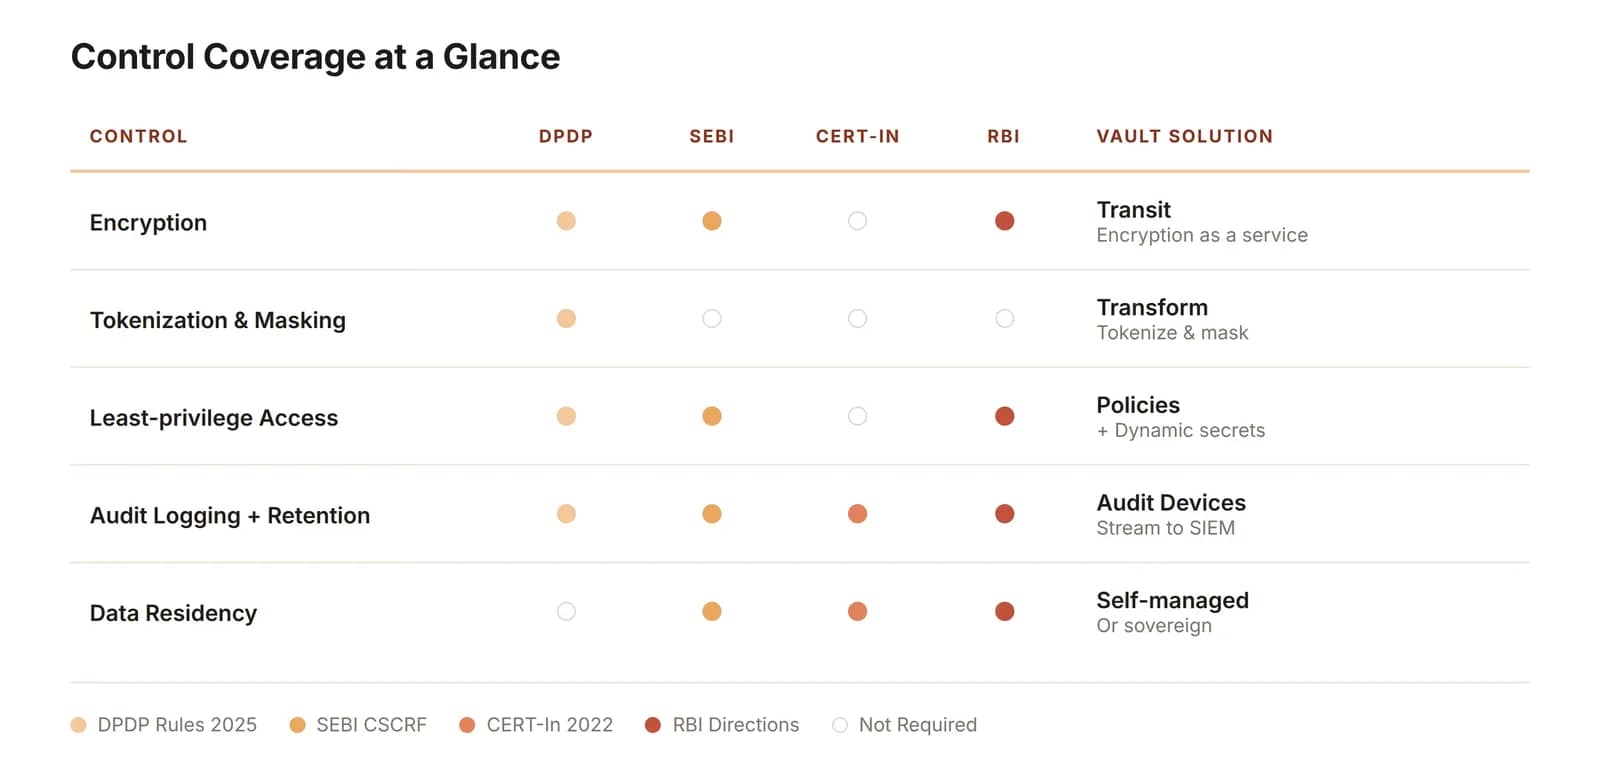
Learn more about how India’s data protection and cybersecurity rules are converging.
HashiCorp Vault Enterprise advances AI agent security with recent enhancements now generally available.
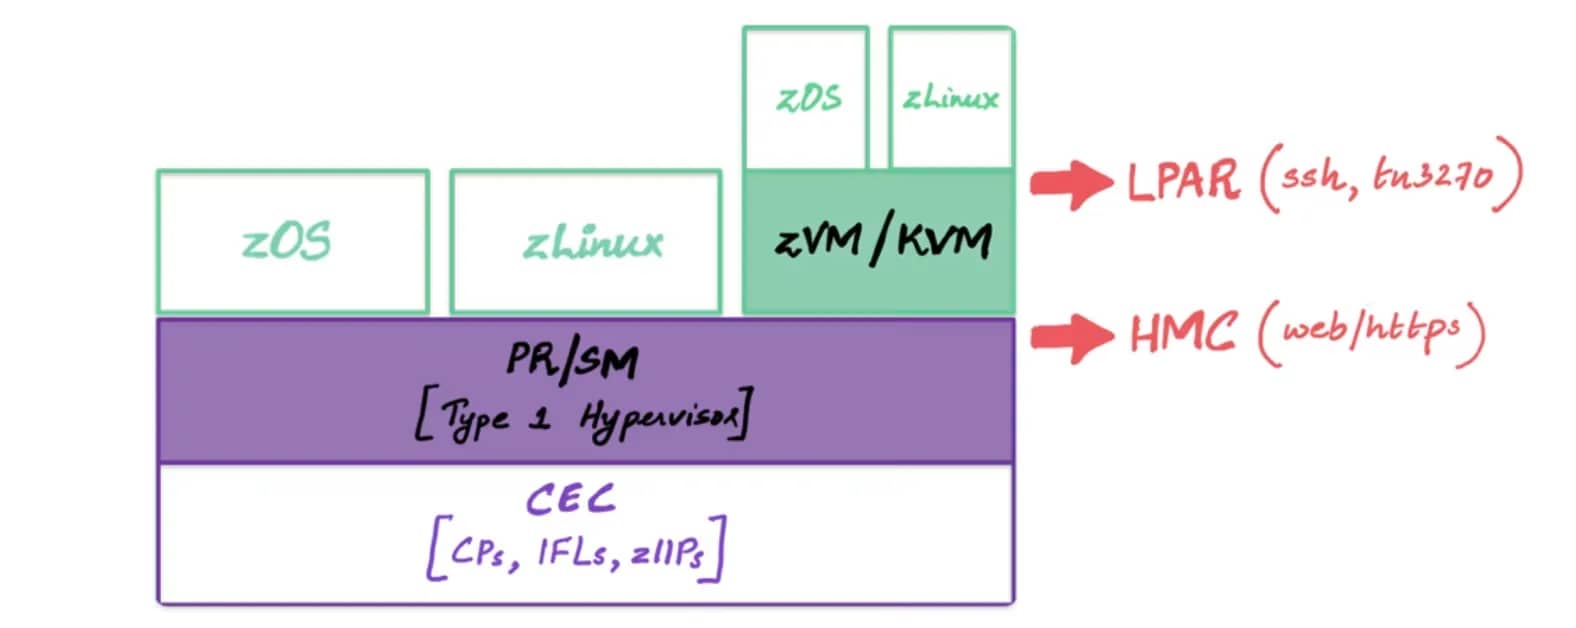
HashiCorp Boundary modernizes mainframe access with identity based controls, JIT credentials, and central auditing via a mainframe adjacent worker.
Learn how the refreshed HashiCorp Validated Designs help teams find field tested guidance for deploying, operating, and using products in production.
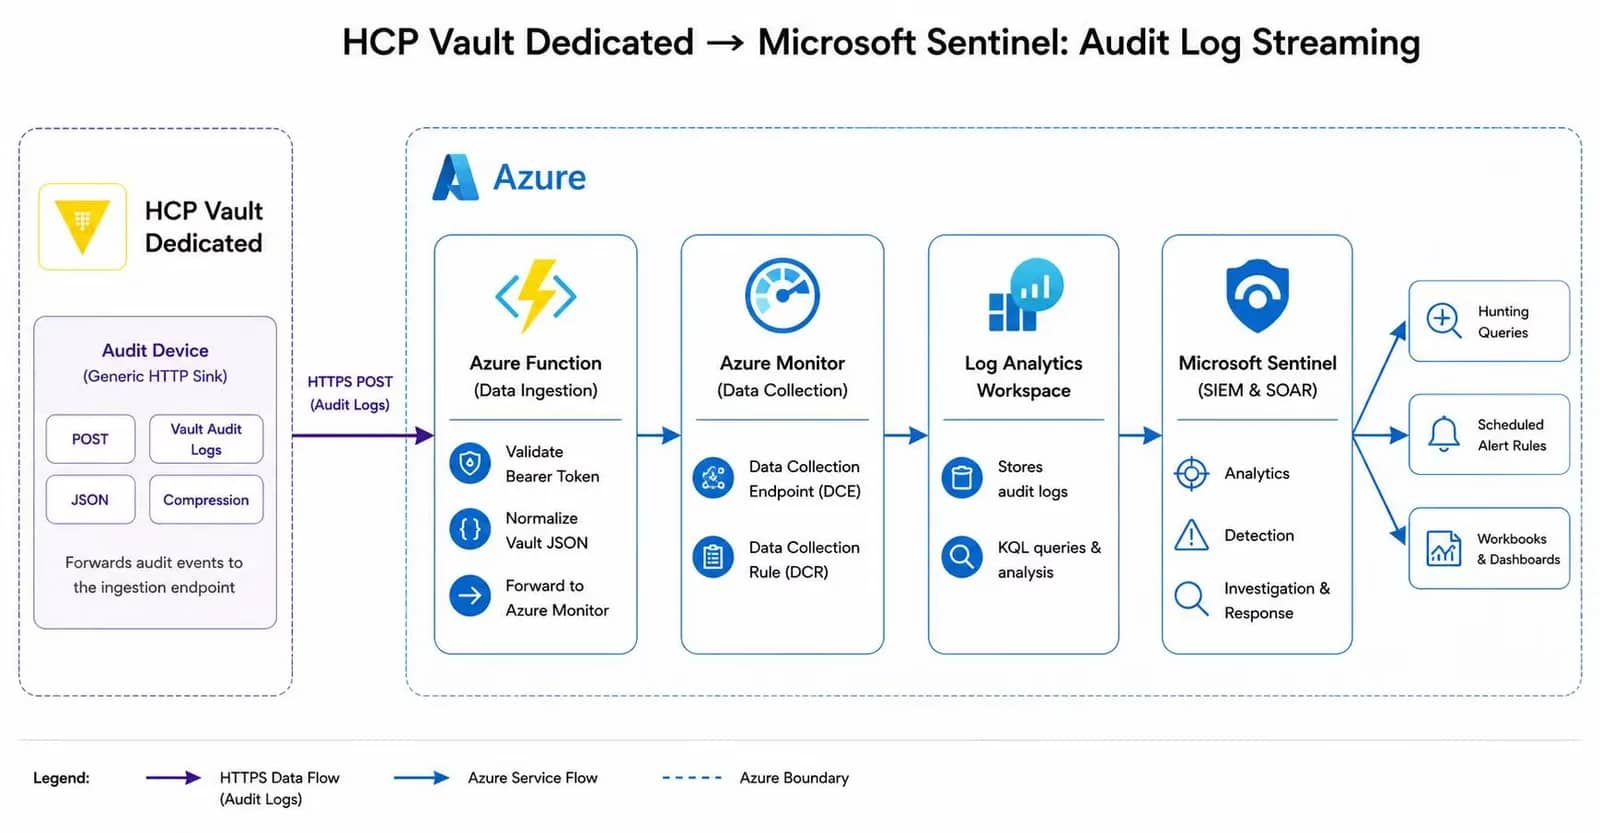
HCP Vault Dedicated has no native Microsoft Sentinel connector. Deploy a Terraform managed pipeline that streams audit logs into Azure Log Analytics and Microsoft Sentinel.
New HCP SCIM provisioning automates user and group lifecycle management from your identity provider to reduce admin overhead and improve secure, consistent access.
Packer v1.16.0 adds native SLSA provenance generation and verification for machine images, along with new HCL2 features for provisioners and variables.
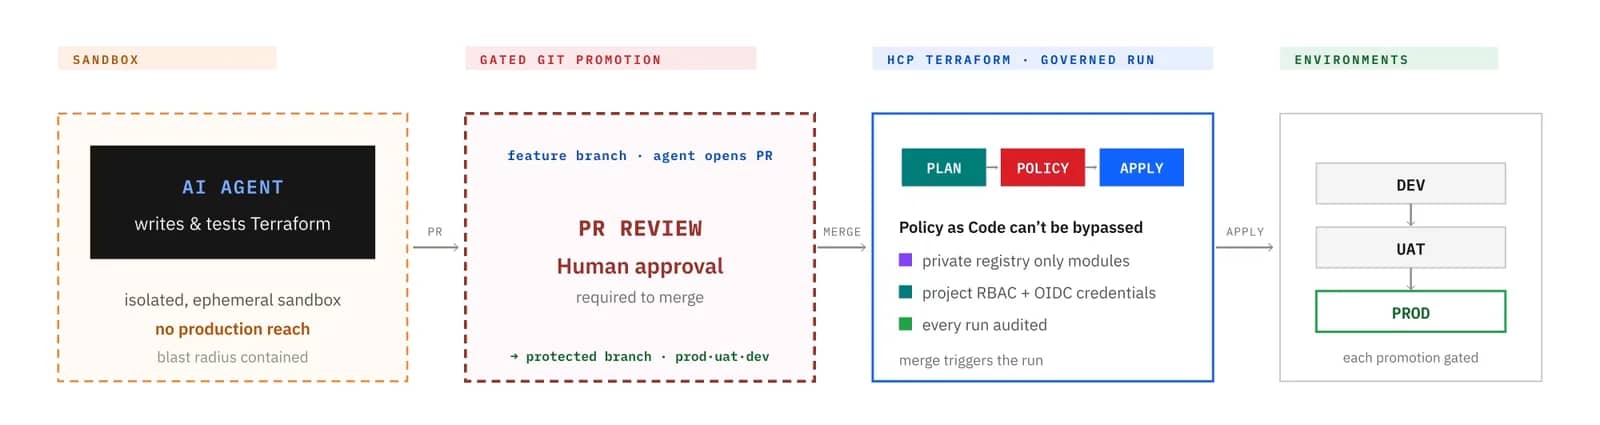
AI agents author and run Terraform on their own. HCP Terraform makes autonomy accountable: provenance, policy, identity, isolation, and audit.
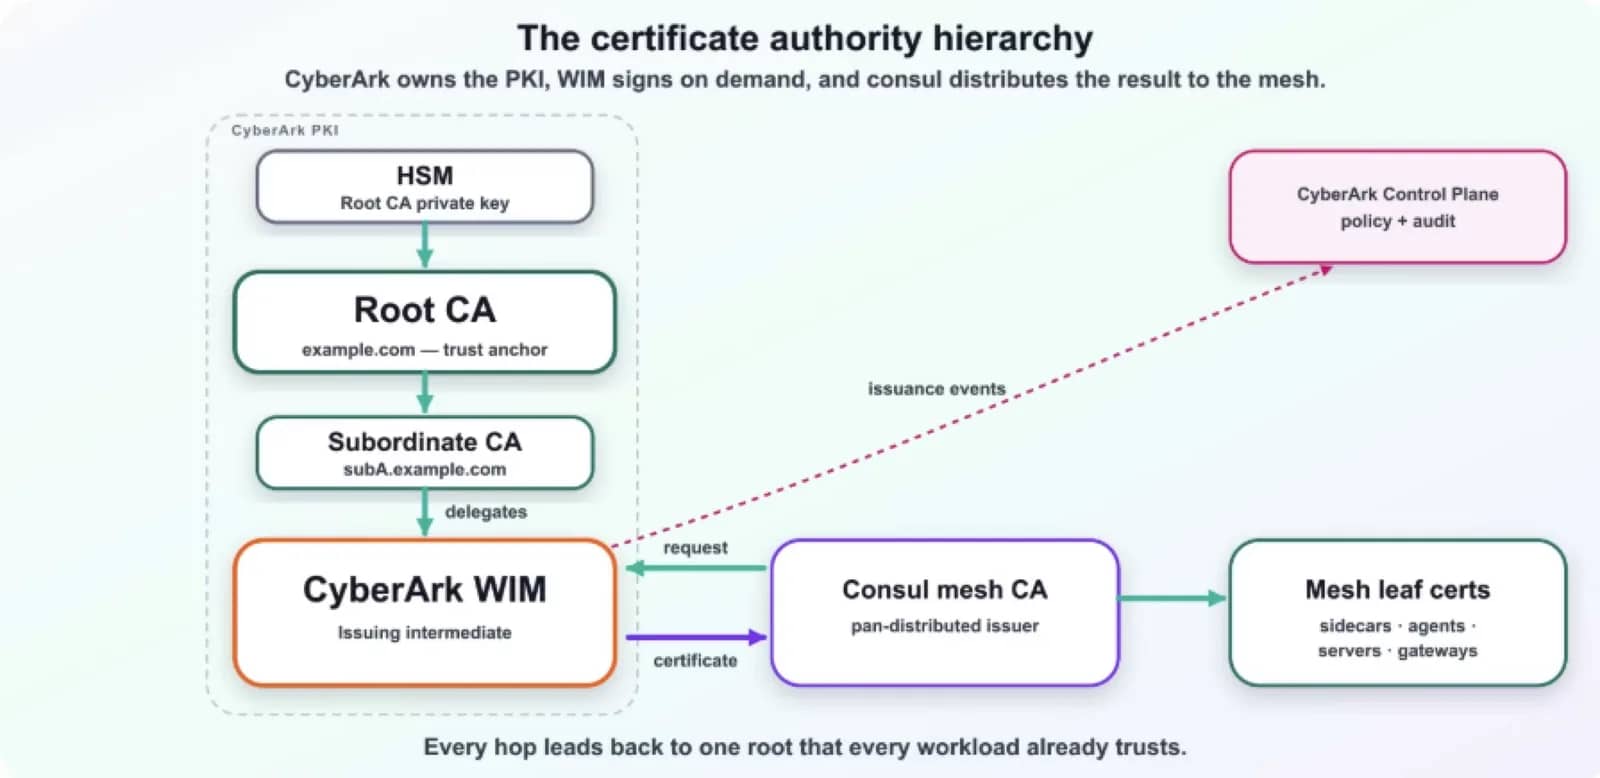
Consul Enterprise 2.0 lets you use CyberArk Workload Identity Manager as an external CA for the mesh, anchoring trust in PKI your security team already governs.
Terraform AzureRM provider 5.0 adds more control over Resource Provider registration, opt in Azure preflight validation, and a cleaner base for future development.
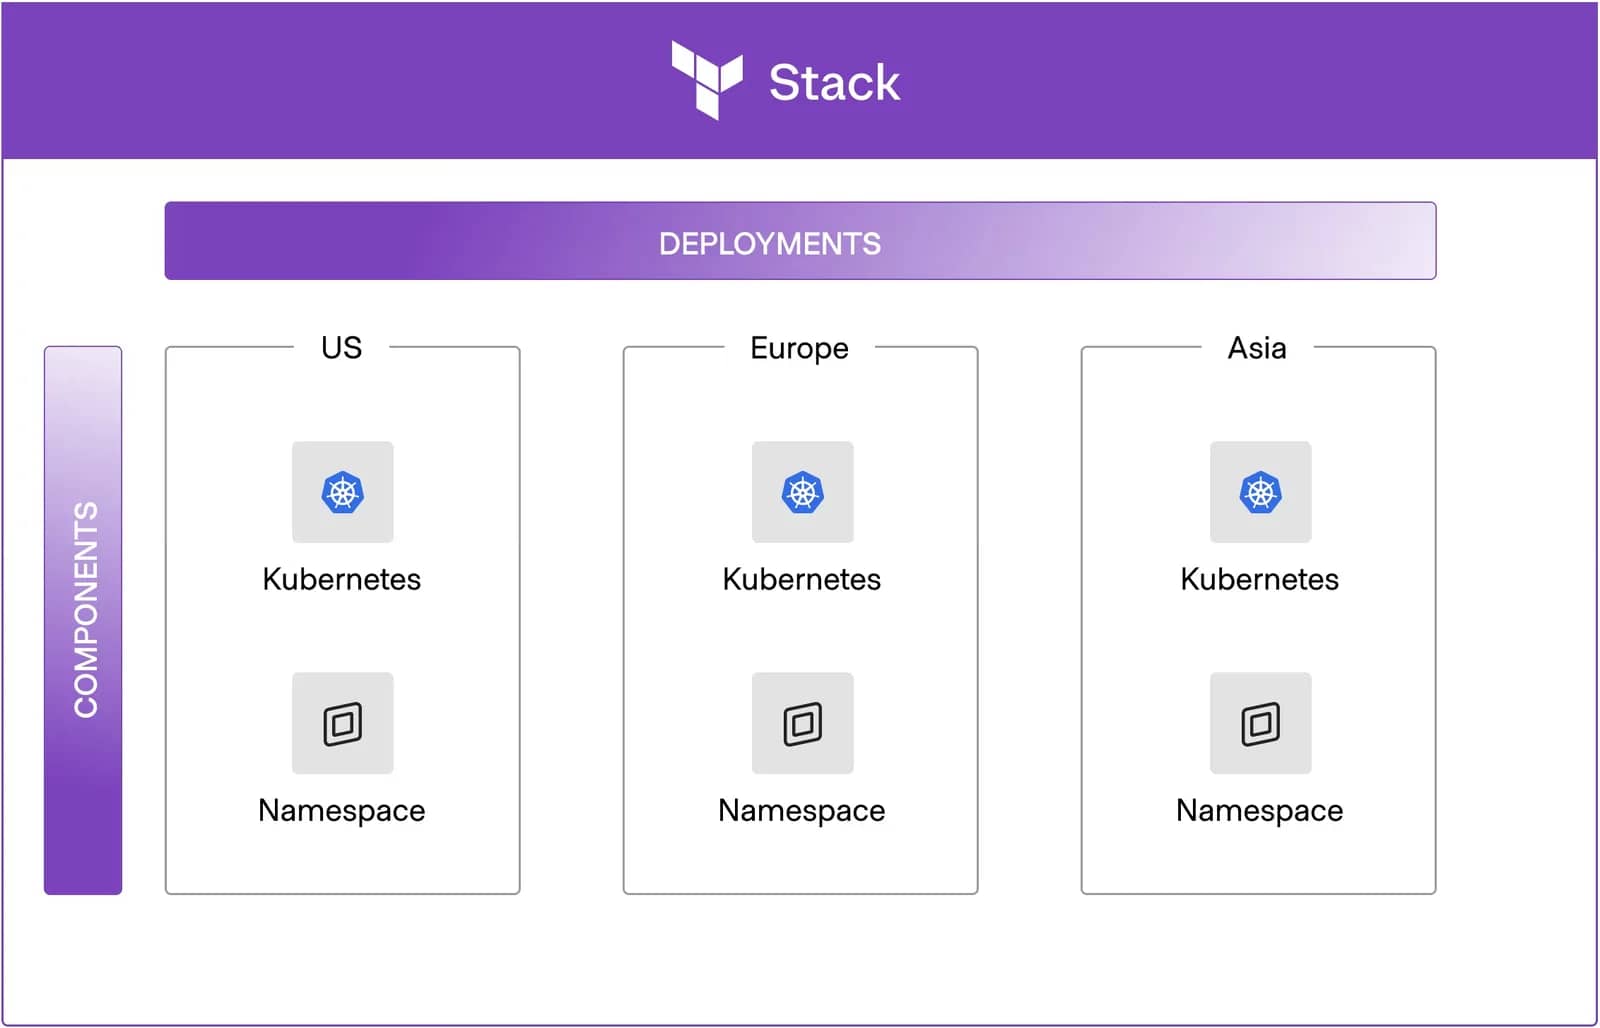
Terraform Stacks simplify provisioning and managing resources at scale, reducing the time and overhead of managing infrastructure.
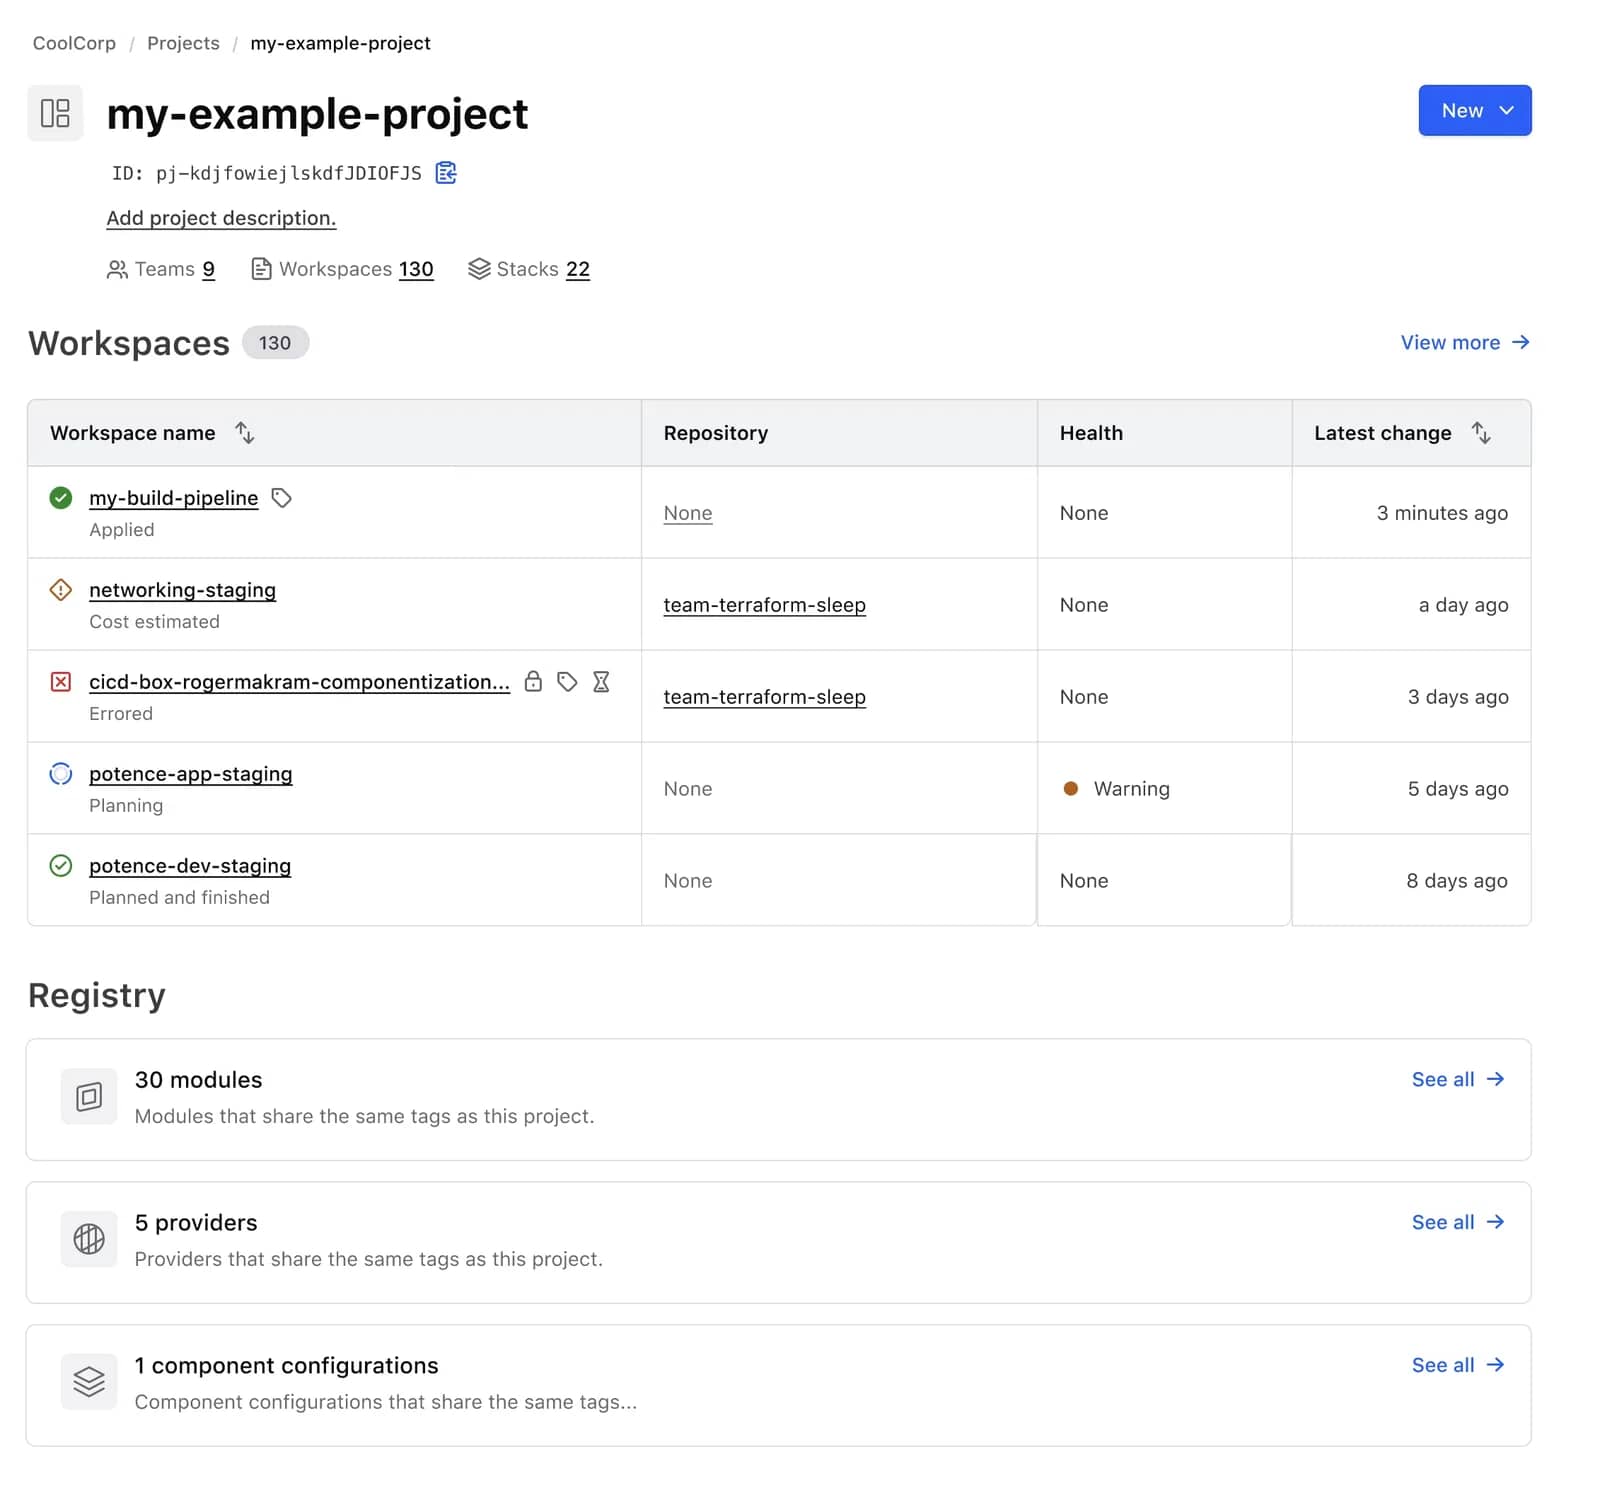
HCP Terraform and Terraform Enterprise boost resiliency, governance, and scalability, helping platform teams manage infrastructure and deliver faster at scale.